CleverSpeed Resources
What Is SASE and Why It Matters for Your Business
← All resources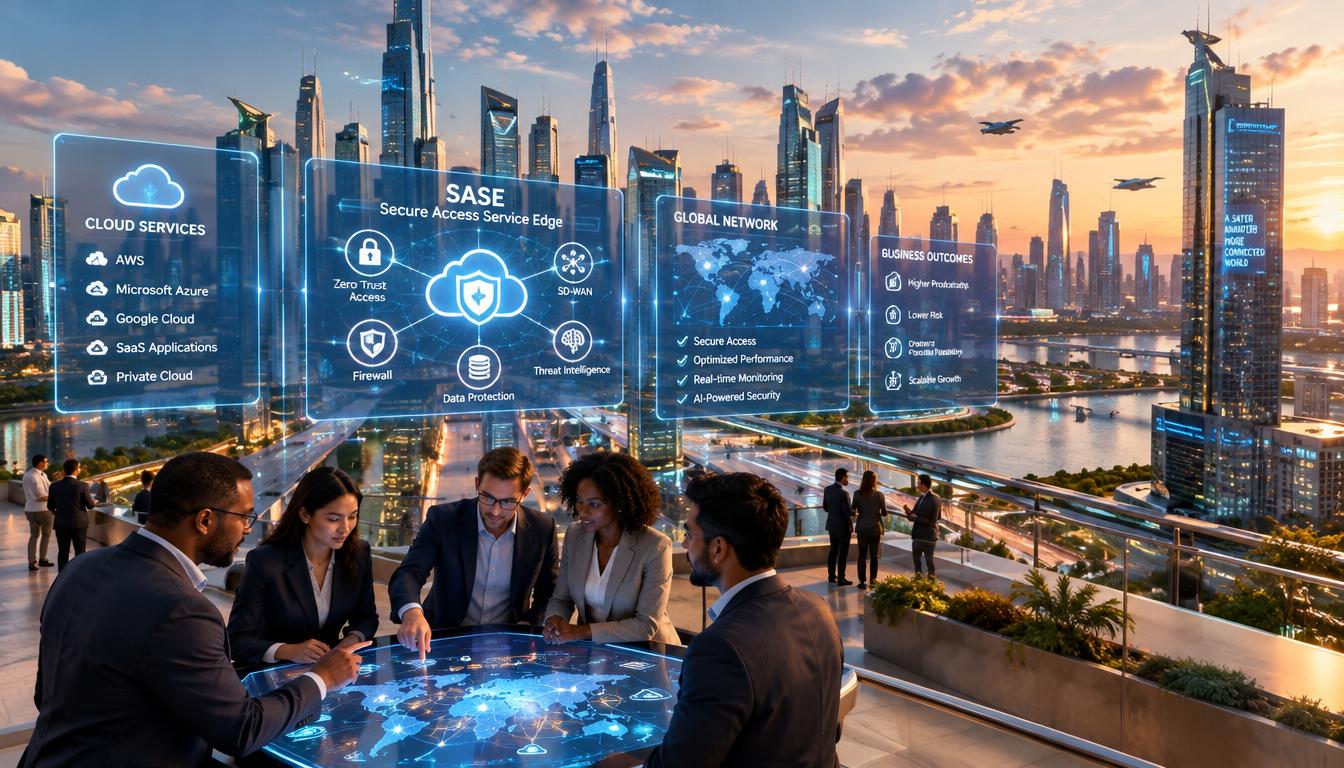
The global market for SASE is projected to reach $28.5 billion by 2028, growing at 26% each year. That pace reflects a major shift: enterprises need reliable access and strong security as work, applications, and data move beyond the office.
Gartner introduced the term in 2019 for a cloud-delivered framework that brings network connectivity and security together. Instead of relying on one office perimeter, it protects users wherever they connect, including across Singapore and regional operations.
Its architecture can combine SD-WAN, SWG, CASB, FWaaS, and ZTNA. Together, these services help manage traffic and apply security controls across cloud platforms, business applications, and devices. The service edge can support a clear access policy while giving teams more flexibility in how they connect.
For Singapore enterprises, the right solution must also support compliance, data sovereignty, and operational trust. We’ll explain the key terms and design choices so decision-makers can assess secure access, networking security, and architectural fit without losing sight of business needs.
Key Takeaways
- SASE joins network access and security in a cloud-delivered framework.
- Gartner introduced the term in 2019 to address distributed access needs.
- SD-WAN, SWG, CASB, FWaaS, and ZTNA can work together in one design.
- Security controls can follow users beyond a fixed corporate location.
- Singapore enterprises should weigh compliance, sovereignty, and flexibility.
What Does sase Mean?
Secure Access Service Edge combines networking and security in a cloud-delivered model. Gartner defined the framework in 2019 for organizations with distributed users and business-critical services. This SASE model helps teams apply consistent access rules across locations, rather than relying on a fixed data-center perimeter.
How Secure Access Service Edge Combines Networking and Security
Instead of adding security as a separate network layer, the architecture brings SD-WAN together with cloud services: SWG, CASB, FWaaS, and ZTNA. These components can enforce policy at an edge near users and applications. For a closer look, explore this Secure Access Service Edge overview.
- SD-WAN steers traffic across sites and cloud resources.
- Security services inspect web activity and protect data.
- Zero trust network access grants access based on identity and context.
Why Gartner Introduced the Framework
Cloud adoption, SaaS use, and remote work changed how people reach business applications. Gartner’s 2019 framework addressed that shift by joining networking with security in one service edge. A consistent trust policy can help govern access across devices and locations. See this architecture overview for more detail.
Why SASE Matters to Modern Businesses
Legacy on-premises controls and separate security tools can leave gaps when users work across offices, homes, and cloud applications. Teams may struggle to apply one policy to every connection, which can expose sensitive data and limit network visibility.
Remote work and cloud adoption have changed how people reach business services. SASE brings networking and security into a shared architecture, helping teams manage traffic across users and branches. A cloud-delivered edge can adapt as access needs shift, without tying every control to one location.
“Market growth signals demand, not guaranteed results.”
The market is projected to reach $28.5 billion by 2028, with a 26% CAGR. This forecast points to rapid enterprise adoption; it does not promise the same outcome for every solution. We recommend assessing fit, data handling, and operational needs.
For Singapore organizations, a unified platform can improve visibility and support consistent network security. Pairing access rules with zero trust principles can also strengthen trust in how users reach applications.
| Business challenge | Operational impact | Unified approach |
|---|---|---|
| Fixed controls | Remote access can vary by location. | Apply consistent policies across connections. |
| Separate tools | Gaps can reduce data visibility. | Coordinate security services and management. |
| Changing traffic | Branches may rely on central routes. | Adapt cloud access as needs change. |
How SASE Architecture Delivers Secure Access
A connection begins when a user requests a business resource. The SASE platform sends that traffic to a nearby cloud point of presence (PoP), where security controls check the request before granting access. This service edge can connect users to cloud, SaaS, or private data center resources.
Cloud Points of Presence Connect Users to Resources
Distributed PoPs bring networking and security enforcement closer to users than a headquarters-only design. For Singapore teams, this can support reliable network access across regional offices and remote locations. The architecture routes each request based on its destination and approved access rules.
Centralized Policies Govern Users, Devices, and Traffic
A central policy can consider identity, device context, and traffic type before users reach applications. One management plane gives IT teams a shared view of users, devices, branches, and application access. This helps teams oversee data flows and apply security controls across services.
- Verify user identity and device status.
- Route traffic to approved resources.
- Apply the relevant security policy.
Cloud delivery alone does not ensure consistent enforcement. Teams must design the architecture, configure policies, and test each service edge. With deliberate management, SASE can support secure access while keeping trust decisions clear.
Core SASE Components and Their Roles
A strong design assigns clear roles to each component. SD-WAN manages network paths, while security services inspect access and protect data. Together, they form an architecture that can serve Singapore teams across offices, remote locations, and cloud resources. Read our secure access service edge overview for context.
SD-WAN Routes and Optimizes Network Traffic
SD-WAN uses dynamic path selection to send traffic over available connections. It can prioritize applications that need steady performance, such as voice or business systems. This networking role differs from security enforcement.
Security Service Edge Includes SWG, CASB, and FWaaS
The security service edge brings together a secure web gateway (SWG), a Cloud Access Security Broker (CASB), and Firewall as a Service (FWaaS). SWG filters internet traffic and blocks risky content. CASB governs cloud application use, adds visibility, and can support data loss prevention. FWaaS replaces physical appliances with cloud firewalls that offer Layer 7 and next-generation firewall capabilities.
ZTNA Provides Identity-Based Access to Applications
Zero trust network access (ZTNA) grants verified users access only to authorized private applications. It can keep checking user and device context as sessions continue. Integrating these controls with SD-WAN creates a coordinated solution, not a collection of isolated tools.
“Route with purpose; grant access with evidence.”
| Component | Primary role | Enterprise value |
|---|---|---|
| SD-WAN | Selects and prioritizes network paths | Supports application performance |
| SWG, CASB, and FWaaS | Filter web use, govern cloud apps, inspect traffic | Improves visibility and protection |
| ZTNA | Verifies identity and device context | Limits access to approved applications |
How SASE Applies Zero Trust to Network Access
Zero trust does not treat a person or device as safe just because it connects from a familiar network. Location alone cannot prove identity or protect business data.
Zero trust network access (ZTNA) checks a user’s identity and device context before it grants access to private applications. It connects users to approved resources, rather than opening a broad path into the corporate network.
A VPN tunnel may place a user on a wider network. By contrast, ZTNA limits access to specific applications. Least-privilege rules reduce exposure to unauthorized systems and can limit lateral movement.
- Verify identity before granting access.
- Check device context and security status.
- Allow only the resources needed for the user’s role.
For Singapore enterprises, the architecture still needs careful configuration. Clear policies, continuous verification, and ongoing monitoring help keep security controls effective across cloud services and network traffic. We recommend reviewing access rules as applications, devices, and business needs change.
Business Benefits of a Unified SASE Platform
A unified SASE platform can reduce point-product complexity by bringing networking and security services into one management model. This can help IT teams coordinate policy changes and avoid gaps between separate tools. Explore our secure access architecture overview for more context.
Centralized visibility gives teams a clearer view of users, applications, and network edges. They can apply a shared policy across cloud access and office connections. This supports more consistent network security and helps teams oversee data flows.
SD-WAN can steer traffic across available paths to support application performance for distributed users. A usage-based licensing model may also reduce reliance on capital-intensive hardware and make operating expenses more predictable.
These benefits depend on sound design and implementation. We recommend matching the architecture to operational needs, compliance duties, and the organization’s approach to zero trust. A unified platform is a means to those outcomes, not a guarantee.
| Area | Potential benefit | Key consideration |
|---|---|---|
| Management | Unified controls and clearer visibility | Define ownership and policy rules |
| Network performance | Traffic paths can support application needs | Test routes and service quality |
| Cost model | Flexible licensing may shift spending to OPEX | Review usage and operating requirements |
Common Enterprise Use Cases for SASE
Enterprise deployments often focus on two needs: supporting work across locations and protecting business data. For Singapore organizations, a well-planned secure access architecture can help apply clear rules across users, devices, and services.
Secure Hybrid Workforces and Branch Locations
Hybrid teams need reliable network access without relying on one office perimeter. Zero trust network access (ZTNA) can grant each user access to approved resources. A SaaS company reported deploying remote access five times faster after replacing legacy VPN technology with ZTNA.
A technology company also reported enabling 320,000 employees to work remotely within two weeks, while cutting management and operating costs by 70%.
Protect Cloud Applications and Prevent Data Loss
Branch offices need consistent controls as traffic moves between local sites and cloud applications. One food-and-beverage company reported preventing 4 million policy violations and blocking 14,000 threats each month. After retiring legacy VPNs, it also saved 70% on hardware, updates, and licensing.
These results are company-reported, not guaranteed outcomes. Teams can combine a secure web gateway with a cloud access security broker to monitor web use, govern applications, and support data loss prevention.
SASE and SSE: Understanding the Difference
Choosing between SSE and SASE starts with understanding what each model covers. Security service edge (SSE) brings together cloud-delivered security services, such as secure web filtering, cloud application controls, and zero trust access security. It focuses on protecting users, data, and applications.
The broader service edge model combines those protections with SD-WAN networking. This adds network path control to the security layer, linking networking and security in one architecture. Read this SASE vs. SSE comparison for more detail.
“Choose the scope that fits your priorities, then plan how each service will work together.”
An SSE-first approach can strengthen security before a full network upgrade. Teams may deploy cloud security services first, then add SD-WAN as resources and business needs allow. This phased route can help Singapore organizations manage change while planning consistent policy and service integration. For related cloud controls, see our CASB and SASE comparison.
The right choice depends on priorities, deployment capacity, and the need to transform the network. Keep the terms distinct: SSE covers security; SASE combines security and networking.
SASE Compared With Legacy VPN and Network Security
Traditional VPNs protect a connection with an encrypted tunnel. After sign-in, the user may join a broad corporate network and reach more resources than the task requires. This model can suit some workflows, but it expands the impact of stolen credentials.
With SASE, cloud-delivered controls evaluate identity and device context, then grant secure access to approved applications. Zero trust network access (ZTNA) follows least-privilege rules; it limits exposure to other systems and can reduce lateral movement. The policy focuses on the application, not broad network membership.
- Legacy design: Hardware at fixed sites often anchors security policies.
- Cloud design: Policies can follow users across offices and remote locations.
Cloud policies help teams apply networking security rules across locations and protect business data. Still, SASE does not remove every risk. Results depend on careful configuration, strong access policies, and ongoing monitoring. We recommend testing controls across applications, devices, and web traffic before a broad rollout.
How SASE Can Support Compliance in Singapore
Singapore enterprises need controls that match their regulatory duties and data-sovereignty requirements. SASE can help teams apply consistent rules across users, applications, and locations. It does not replace legal review or careful compliance planning.
Centralized Policies and Audit Logs Improve Visibility
Central policy enforcement and a unified audit trail give compliance teams a clearer view of access and data movement. Gartner’s examples show how security services can support controls for sensitive information:
- DLP and CASB policies can limit where personal data travels, including uploads to unsanctioned applications.
- Zero trust network access can grant least-privileged access to protected health information (PHI).
- Firewall segmentation can separate payment environments, while a secure web gateway inspects encrypted traffic involving cardholder data.
These measures can strengthen network security and help teams review cloud access across the service edge. Map each policy to the data it protects, the applicable obligation, and where that data may reside. We recommend validating logs, inspection settings, and management processes before relying on them for audits.
“Visibility is useful only when policy, evidence, and data location align.”
Planning a SASE Rollout for Your Organization
A reliable rollout starts with a clear view of your current environment. For Singapore enterprises, we recommend setting priorities before choosing a deployment path; this helps align security, performance, and data needs.
Assess Networks, Applications, and Security Policies
Inventory your network, applications, identity controls, devices, data flows, and policies. Note how traffic moves between branches, remote users, and cloud services. Then identify where secure access matters most and map those needs to the right components.
- Record existing controls and trust network boundaries.
- Prioritize users, applications, and network access needs.
- Confirm ownership for monitoring and policy reviews.
Plan a Phased Deployment for Users and Branches
A gradual rollout gives teams room to validate controls and user experience. Some organizations begin with SSE services, then add SD-WAN as they modernize networking. Pilot the approach with a remote workforce or one branch before expanding.
Set review checkpoints to adjust configuration and management practices. For connectivity planning, compare a Singapore upstream provider against your traffic, resilience, and operational needs. This measured approach supports zero trust goals while keeping the architecture aligned with business priorities.
Choosing a SASE Solution Without Vendor Lock-In
Vendor choice should protect your ability to adapt. In Singapore, that means checking technical fit, policy control, and data sovereignty before you commit.
Compare Integration, Management, and Policy Capabilities
A single-vendor SASE design combines SD-WAN and SSE in one architecture, dashboard, and policy engine. A multi-vendor design can offer flexibility, but teams must connect products and keep policies aligned. Weigh integration effort, operational ownership, and dashboard complexity. Confirm that one platform meets your needs without creating excessive reliance on one provider. For network options, compare SD-WAN companies.
Evaluate Cloud Coverage, Performance, and Data Controls
Check PoP locations, traffic performance, and consistent access for users and branches. Review cloud application visibility and DLP against security and sovereignty rules. A cloud access security broker can help govern app use; confirm its controls fit your security service model.
- Test coverage, latency, and policy consistency.
- Review data controls and access security needs.
- Require exit options, interoperability, and portability.
Plan for change from the start. Clear exit terms help your network evolve without avoidable lock-in.
| Evaluation area | Single vendor | Multi-vendor |
|---|---|---|
| Policy management | One shared engine | May need synchronization |
| Operations | Fewer dashboards | More integration work |
| Future flexibility | Check exit terms | Check interoperability |
Conclusion
For Singapore enterprises, SASE offers a cloud-delivered model that brings networking and security together. It helps users reach business applications across locations. Gartner introduced the framework in 2019 to meet the needs of distributed workforces and business-critical systems.
SD-WAN and SSE capabilities work together at the service edge. ZTNA checks identity and grants least-privilege access to approved resources, helping protect sensitive data. The global market forecast reaches $28.5 billion by 2028, with a 26% CAGR; this signals momentum, not guaranteed results.
Before selecting a platform or solution, assess your architecture, compliance duties, data sovereignty needs, deployment phases, and vendor portability. We recommend testing policy enforcement and exit options against real workloads. This deliberate review can align secure access with your operational and regulatory priorities.
FAQ
What does SASE mean?
SASE means Secure Access Service Edge. It brings networking and cloud-delivered security services into one architecture, so organizations can connect users to applications with consistent controls.
How does this architecture support zero trust?
Zero trust checks identity, device status, and policy before granting access. It limits each user to approved resources instead of trusting a network connection by default.
What is the difference between SASE and SSE?
Security Service Edge, or SSE, focuses on cloud-delivered security. SASE combines SSE with networking capabilities such as SD-WAN to manage connectivity and protection together.
Which security tools may a SASE platform include?
Common services include a secure web gateway, a cloud access security broker, and firewall capabilities. These tools can inspect web traffic, apply data loss prevention rules, and protect cloud applications.
Can SASE replace a traditional VPN?
It can reduce reliance on broad VPN access by granting identity-based access to specific applications. Some organizations keep VPNs during migration or for systems that need them.
How can SASE support compliance in Singapore?
Central policies and audit logs can improve visibility into access and data handling. Organizations should assess data location, retention, and provider controls against obligations such as Singapore’s PDPA and applicable MAS requirements.
How should an organization plan a SASE rollout?
Start by mapping users, devices, branches, applications, and current policies. Then deploy in phases, test performance and controls, and refine the design before broader adoption.
How can we reduce vendor lock-in when choosing a solution?
Review interoperability, policy portability, management options, and cloud coverage. Confirm how the provider handles data controls and whether the design supports your existing network and future needs.